HIGH-STAKES SELF HOSTING
A password server you cannot restore is worse than a hosted vault.
A password manager stores the keys to everything else. Bitwarden will host that vault. Bitwarden lite and the standard server let you host an official build. Vaultwarden is a separate project that speaks the Bitwarden client protocol. None of these remove the need for a written recovery plan.
Reviewed 30 October 2026 against Bitwarden's deployment articles and the Vaultwarden project documentation. This guide does not quote a Bitwarden subscription price. How we treat unchecked prices.

What self-hosting a vault actually changes
On Bitwarden's hosted service, Bitwarden runs the servers, the uptime and the updates. You still choose a strong master password, turn on a second factor, and keep an emergency access plan. You do not patch Docker at midnight.
On a server you run, you can place the vault on hardware you control. You also become the person who notices that HTTPS expired, that the disk filled, or that a new phone cannot log in because the server is off. Clients that have already synced keep a local copy, so a short outage does not empty a phone that unlocked the vault yesterday. A brand new phone has nothing cached. If the server is down, that phone cannot download the vault. Plan for that before you travel.
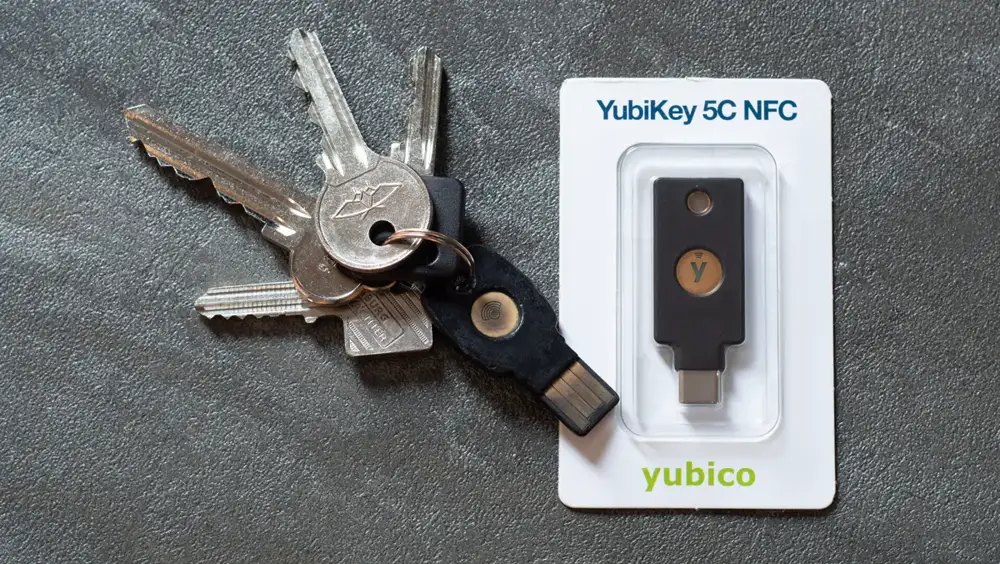
A hardware security key, such as the one in the photograph, is a second factor. It does not replace the master password, and it does not replace a backup of the vault. Store a spare key, or a one-time recovery method, somewhere that is not the same keyring as the only key that can get you in.
Official servers and Vaultwarden
Bitwarden documents two self-hosted shapes. The standard Linux deployment expects an x64 processor, at least 1.4 GHz and preferably a 2 GHz dual core, at least 2 GB of RAM with 4 GB recommended, and at least 12 GB of disk with 25 GB recommended. It wants Docker Engine 26 or newer, with Compose. The default database container is SQL Server Express, with a 10 GB database size limit that does not need a separate SQL licence. You can point it at an external database instead.
Bitwarden lite, which replaced the unified beta in December 2025, is the smaller official image for personal and home-lab use. Bitwarden says it is not the business deployment. The published minimums are 200 MB of RAM, 1 GB of storage and Docker Engine 26 or newer. The image is ghcr.io/bitwarden/lite. It does not ship a database inside the application container. You choose SQLite, PostgreSQL, MySQL or MariaDB, or SQL Server. SQLite can create vault.db under the /etc/bitwarden volume. You also need an installation id and key from bitwarden.com/host. The container will use more than 200 MB unless you cap it. The documented cap is docker run --memory=200m or Compose mem_limit: 200m, and Bitwarden says 200m is the floor for that cap.
Vaultwarden is not Bitwarden. It is an independent server, written to work with Bitwarden clients, and it is the project you get from the Vaultwarden images on Docker Hub, GHCR or Quay. The project says the web vault needs HTTPS, because the browser's Web Crypto API needs a secure context. Their example publishes the container only on localhost and expects a reverse proxy:
docker pull vaultwarden/server:latest
docker run --detach --name vaultwarden \
  --env DOMAIN=https://vw.example.com \
  --volume /vw-data/:/data/ \
  --restart unless-stopped \
  --publish 127.0.0.1:8000:80 \
  vaultwarden/server:latest
Change the domain. Leave the publish address on 127.0.0.1 and put Caddy, nginx or another proxy you already understand in front, with a real certificate. A self-signed certificate will fight the mobile apps. After you have created your account, turn off public registration. An open signup on a password server is an invitation. The project wiki documents the setting. Do not leave the default if the default allows strangers to create vaults on your host.
| Option | Who patches the server? | Published hardware floor | Choose it when |
|---|---|---|---|
| Bitwarden hosted | Bitwarden | None in your house | You want the official service and a second factor |
| Bitwarden standard | You, on an official install | 2 GB RAM, 12 GB disk, x64, Docker 26+ | A business or a heavier official install |
| Bitwarden lite | You, on an official image | 200 MB RAM, 1 GB disk, Docker 26+ | A personal vault on a small home server |
| Vaultwarden | You, on an unofficial project | A container and a data directory. HTTPS is mandatory for the web vault | You accept a third-party server and you will update it |
Three picks
Bitwarden's hosted service
This is the default for a household. You get official clients, official updates and a server that stays up when your home connection does not. Add a hardware key or another second factor, and export an emergency copy to somewhere you can reach if Bitwarden the company is having a bad day. That export is your backup. The hosted vault is still one provider.
Bitwarden lite at home
Choose lite when you want the official image, a Pi or a mini PC is already on, and the vault is personal. Use SQLite only if you will stop the container before you copy vault.db. Use PostgreSQL if you already run it well. Generate the installation id rather than copying one from a blog. Put HTTPS on the hostname in BW_DOMAIN. A vault served over plain HTTP on a port forward is the failure mode this pick exists to avoid.
Vaultwarden, with your eyes open
Choose Vaultwarden when you want the lighter unofficial server and you will read its release notes. You do not get Bitwarden's support for that container. Update it when the project updates, because password-server bugs are not the kind you leave for a quiet month. Back up /vw-data while the container is stopped so SQLite is not mid-write. Restore that directory onto a spare machine and log in before you call it a backup.
A backup you can use from a different building
Stop the container. Copy the data directory, including the database file and any attachments. Copy the reverse-proxy config and the environment file only if you understand that the environment file contains secrets. Store the copy off the server, encrypted. Then start the service again.
docker stop bitwarden
# copy the data directory to the backup disk, then:
docker start bitwarden
Use the container name you actually chose. For Vaultwarden that is often vaultwarden. The restore drill is: a laptop that has never signed in, a copy of the backup, and the master password from memory or from a paper copy in a drawer. If the only copy of the master password is inside the vault, you have built a lock with the key inside. Write the master password down and store the paper away from the server. A password manager that forbids paper is how people get locked out.
Also export an encrypted JSON from a client on a schedule you will keep, such as the first weekend of the quarter. That export still opens if the server build will not start. It is a second format, which is the point.
HTTPS, updates and the port you must not forward
Bitwarden lite's example maps port 80 on the host to 8080 in the container. That is a starting layout, not a finished one. Terminate HTTPS at a proxy, or enable the certificate options Bitwarden documents, and do not leave the admin surface on the open internet without it. Vaultwarden is stricter in the README: the web vault simply will not do cryptography in an insecure context.
Update on purpose. For lite, the documented path is docker stop, docker rm, docker pull ghcr.io/bitwarden/lite, then docker run again with the same volume and env file. Compose users pull and recreate. Read the release note before you pull latest on the day you are travelling. A vault upgrade is a poor airport activity.
Share the vault with a partner only after they have their own second factor and you have tested emergency access. A shared master password on a sticky note is not a family plan. Bitwarden's organisation and emergency-access features exist so that one person's absence is not a lockout. Turn them on while everyone is calm.
Questions people skip
Is Vaultwarden the official lite server?
No. Lite is ghcr.io/bitwarden/lite. Vaultwarden is a different project. Both can sit behind Bitwarden clients. Support, licence and update channels are not the same.
Is 200 MB enough for lite?
It is the published minimum, and the memory cap Bitwarden documents. The container uses more if you do not cap it. A home server that also runs Immich should not assume the vault fits in the leftovers without looking at docker stats.
Can I run this on a Raspberry Pi?
Lite is documented as able to run on ARM, which is why Pi and NAS boards are mentioned. The standard deployment's published CPU floor is x64. Vaultwarden publishes multi-arch images, including boards as small as a Pi, and the wiki is where to check the current tag. A Pi that is also your only DNS and your only photo server is a lot of failure in one power supply.
What if I forget the master password?
Nobody can reset it for you, by design, if the vault is encrypted with that password. The recovery is the paper copy or the emergency contact you set up beforehand. A hosted service does not get to bypass that encryption either.
Verdict
Use Bitwarden's hosted service unless you specifically want the server in the house and you will back it up. If you self-host, prefer Bitwarden lite for a personal vault and the standard deployment when you need the supported business install. Use Vaultwarden only as a conscious choice of an independent server, with HTTPS, a localhost publish, registration closed, and a restore you have done once. A hardware key is an extra factor. It is not the backup.
Sources checked 30 October 2026: Bitwarden lite, standard Linux deployment, Vaultwarden, and Vaultwarden images.